
By Samantha Cornwell
Through applied work in risk-based test prioritization, defect prediction, and AI governance, Sai Kumar Gunda’s research shows how core banking platforms can move faster through continuous delivery without losing control over defect containment, security assurance, and audit readiness.
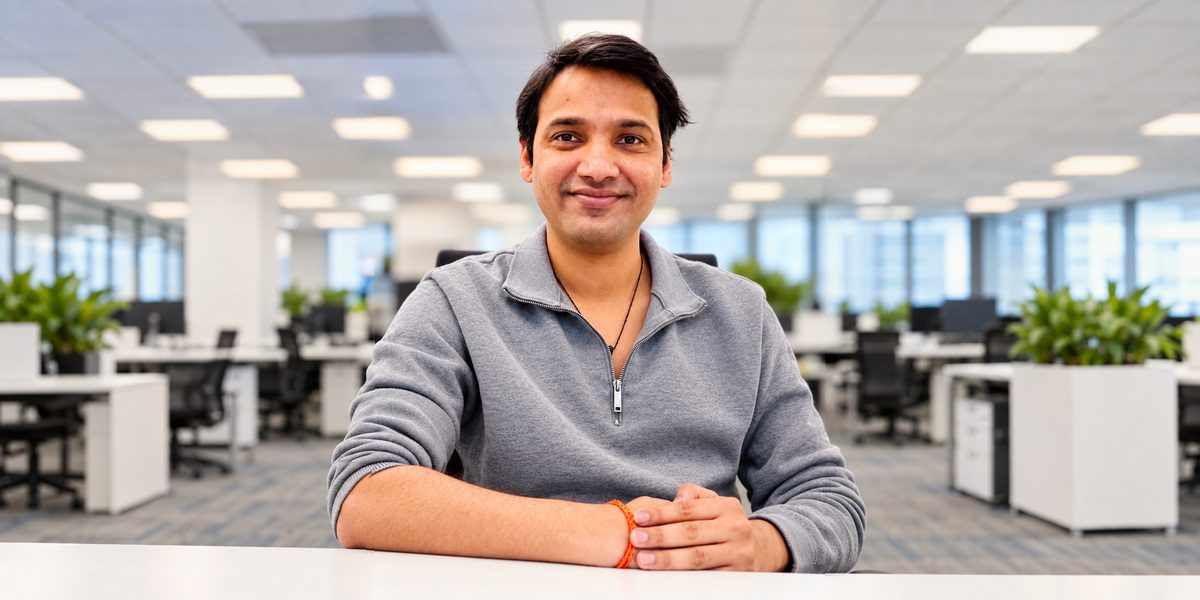
Every release inside a core banking platform carries a quiet risk calculation. A new build might touch a payment rail, a compliance rule, a fraud model, or a legacy batch job that has run unchanged for a decade. Somewhere behind the scenes, a testing team has to decide what to test, how deeply, and how quickly, knowing that the platform cannot simply be paused while the checking happens. That is the operating environment in which Sai Kumar Gunda, a Software Quality Analyst specializing in AI-powered banking and financial systems for major global banking institutions, has built much of his research. His latest publication, “A Risk-Aware AI Framework for Automated Testing and Quality Assurance in Core Banking Systems,” addresses a problem that has become more urgent as banks adopt continuous delivery: how does a testing organization keep pace with constant change without quietly accumulating risk it cannot see?
Who Is Sai Kumar Gunda and Why Core Banking Testing Is Under Pressure
For more than a decade, Gunda has worked on quality assurance and compliance testing for major global banks. His research consistently returns to a single tension: banking platforms are under pressure to release faster, yet they operate under some of the strictest availability, integrity, and regulatory expectations of any industry. Traditional quality assurance, built around fixed test suites and manual triage, was designed for a slower release cadence. As core banking systems evolve through continuous delivery, vendor updates, and increasingly complex integration landscapes, those older approaches struggle to keep defect containment, security assurance, and audit readiness intact.
Test suites grow faster than the teams that maintain them, and the dependencies between systems multiply. Gunda’s framework is a direct response to that gap.
“The underlying idea is to stop treating testing as a fixed checklist and start treating it as a continuous risk calculation,” Gunda explains. “Every change to a core banking system carries a different mix of operational, cybersecurity, compliance, and model risk. If the testing strategy does not reflect that mix, teams end up spending equal effort on low-risk and high-risk changes, which is exactly backwards.”
“Testing in banking cannot just ask whether the software works. It must ask what happens if it fails, who is affected, and how quickly that failure would be noticed.”
What the Risk-Aware AI Framework Actually Does
That reframing sits at the center of the framework described in his research. Rather than scoring test cases in isolation, the system continuously converts operational, cybersecurity, compliance, and model risk signals into concrete test strategy decisions, so that test selection, prioritization, and governance stay aligned with the constraints unique to core banking. As risk signals shift, so does the testing plan.
The framework is built from four integrated components. The first is risk-driven change impact analysis, which traces how a proposed change ripples across a bank’s interconnected systems before a single test is run. The second brings in AI-based defect propensity and failure propagation signals, using historical defect and incident data to estimate where problems are most likely to emerge and how far they could spread if left uncaught. The third is policy-aware test orchestration with verifiable control mapping, which ties test execution directly to the compliance controls it is meant to satisfy, so that coverage decisions can be traced back to specific regulatory or internal policy requirements. The fourth introduces model governance primitives for explainability, robustness, and bias monitoring, extending the framework’s reach beyond conventional software defects into the AI models that increasingly sit inside banking decisions themselves.
“Banks are no longer only testing code paths,” Gunda says. “They are testing models that make judgment calls about customers and transactions. A framework that only checks whether software runs correctly, without checking whether an embedded model is behaving fairly and consistently, is missing an entire category of risk that regulators and customers both care about.”
How the Framework Performed in Testing and Real-World Environments
To evaluate the approach, Gunda ran a simulation-based study comparing risk-weighted prioritization against conventional test scheduling under a fixed execution budget. According to the published results, risk-weighted prioritization improved both time-to-detection and risk-weighted recall, meaning that the highest-impact defects were being caught earlier and more consistently without requiring additional testing capacity. That distinction matters in banking technology, where testing budgets and release windows are rarely negotiable.
A framework that only performs well with unlimited time or unlimited compute is of limited use to a bank that has neither. Gunda’s evaluation was designed specifically around the constraint that testing teams actually face: a fixed budget of execution time and a growing volume of change to cover within it.
The framework was also designed with the reality of banking infrastructure in mind. Core banking environments are rarely uniform. They tend to be hybrid stacks that mix batch processing with real-time online transactions, and legacy mainframe components with newer microservices. A testing framework that assumes a clean, modern architecture quickly runs into trouble once it meets a twenty-year-old settlement job running alongside a containerized fraud-scoring service. Gunda’s approach was built to operate across that mixed environment, rather than treating it as an edge case to be handled later.
Why Audit Readiness and AI Governance Sit at the Center of the Approach
That focus on real-world deployment reflects a broader theme in Gunda’s work. Whether the subject is ATM reliability, anti-money laundering validation, or now automated testing itself, his research keeps returning to the same underlying question: can a system identify what matters quickly enough, accurately enough, and defensibly enough to support real banking operations? For testing organizations, defensibility carries particular weight. A bank cannot simply tell a regulator that its release passed testing; it increasingly has to show which controls were verified, when, and against what evidence.
“Regulators do not ask you to promise that your testing was thorough,” Gunda notes. “They ask you to show it. If a framework cannot produce clear, traceable evidence of what was tested and why, it does not matter how sophisticated the underlying models are. The evidence must be built in from the start, not reconstructed after the fact.”
That evidence-first orientation is what allows the framework to pursue two goals that are often treated as being in tension: reducing unknown-risk exposure while improving release velocity. Traditional thinking often treats thorough testing and fast releases as a trade-off, where more caution necessarily means more delay. Gunda’s research pushes back on that assumption. By concentrating testing effort where risk signals are highest and relaxing it where they are lowest, the framework aims to let low-risk changes move through the pipeline quickly while ensuring that high-risk changes receive the scrutiny and documentation they require.
Gunda’s credentials add context to that trajectory. He holds a master’s degree in information technology and management from Concordia University, St. Paul, and has earned certifications including ISTQB Foundation Level. He is also an active participant in an internal AI Center of Excellence at one of his banking clients, where he contributes to efforts focused on the design and testing of AI tools used in banking operations. That combination of academic grounding and applied, production-level testing experience runs throughout his published research, which has increasingly focused on how AI and automation can be embedded responsibly into the quality assurance practices that keep financial systems dependable.
What Comes Next for Risk-Aware Testing in Banking
Asked what he hopes teams take from the framework, Gunda points back to the discipline required to operate AI responsibly inside regulated environments. “The goal was never to make testing look more advanced,” he says. “It was to make sure that as banks move faster, the risk they are taking on stays visible, measurable, and something they can explain to an auditor, a regulator, or a customer if they ever need to.”
Looking ahead, Gunda expects risk-aware testing to become less optional as banks embed more AI directly into core platforms. Industry analysts have noted that ageing core systems are already limiting how quickly banks can deploy AI while meeting supervisory expectations for real-time risk visibility. Frameworks that convert risk into test strategy, rather than treating testing as a static gate, are likely to become a standard expectation rather than a research contribution.
“The future of quality assurance in banking will not be measured by how many tests are run, but by how well testing effort lines up with real risk,” Gunda says. “Faster releases and defensible risk management are not opposites. They are only in tension when the testing strategy cannot tell the difference between a trivial change and a dangerous one.”
As financial institutions modernize their core platforms, the pressure to deliver faster software updates is no longer separate from the responsibility to manage risk. Gunda’s work treats quality assurance not as a final checkpoint, but as a continuously adapting control layer within the banking technology lifecycle. By combining risk-based test prioritization, AI-driven defect prediction, compliance traceability, and model governance, his framework offers a practical path for banks seeking to improve release velocity while maintaining the evidence, transparency, and discipline required in highly regulated environments.
What makes the approach especially timely is its recognition that banking quality assurance must operate at the same speed as digital transformation itself. As banks adopt continuous delivery, AI-enabled services, and increasingly interconnected platforms, testing teams need more than automation. They need prioritization that can distinguish routine changes from changes that could create operational, compliance, or customer-impact risk. His framework moves beyond traditional test execution by linking quality assurance decisions to business impact, system dependencies, compliance obligations, and AI model behavior, positioning testing as a risk-management function rather than a purely technical activity.